 FM
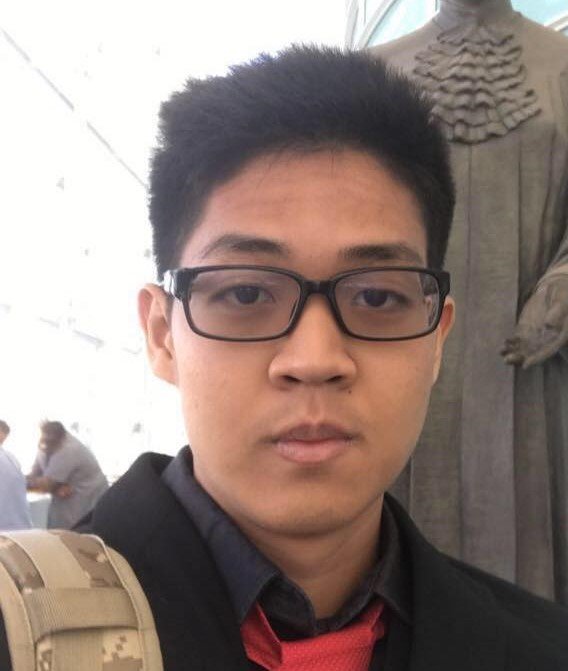
Francis Mendoza
— On the schedule —
When Hallucinations Become Vulnerabilities: Building Reliable AI for Cryptography
This talk presents the design and deployment of a retrieval augmented generation (RAG) support assistant for cryptographic guidance and code generation for Bouncy Castle cryptography libraries. LLMs are a very useful technology, but they do not unilaterally apply to all verticals equally; especially cryptography. Because incorrect cryptographic guidance and/or code can create security risks, the chatbot focused on countering hallucination, ensuring provenance of answers to trusted sources, and verifying the correctness of the cryptographic and citational output. This talk covers system architecture, fail-closed design, challenges for ensuring accuracy of code, cryptographic guidance, and citations, as well as the lessons learned from building and deploying AI-assisted tooling in a security-sensitive environment.
— Compositor's note —
Francis Mendoza is a Filipino-American computer scientist working at the intersection of applied cryptography and resilient distributed systems. He holds a B.S. and M.S. in Computer Science from Arizona State University, where his research focused on cybersecurity for critical infrastructure and autonomous systems. In industry, he is a software engineer at Keyfactor, contributing to both classical and post-quantum cryptosystems within Bouncy Castle: an open-source cryptography library widely deployed across production systems, with millions of downloads. He has previously worked at Fujitsu, the Linux Foundation, Intel, and other companies on cybersecurity research spanning zero-knowledge proofs, blockchain systems, and trusted execution environments.